Encrypted connections
Published systems and custom domains use managed HTTPS certificates and TLS 1.2 or newer, protecting data in transit without relying on users to configure it.
System security
A business system should protect information by design: encrypted connections, controlled access, secure data rules and continuous review — not security added as an afterthought.
Every system we deliver uses a professionally managed security foundation. We then configure access and safeguards around your people, processes, information and level of risk.
Your information stays confidential. We are happy to sign an NDA before any detailed discussion.
The security foundation
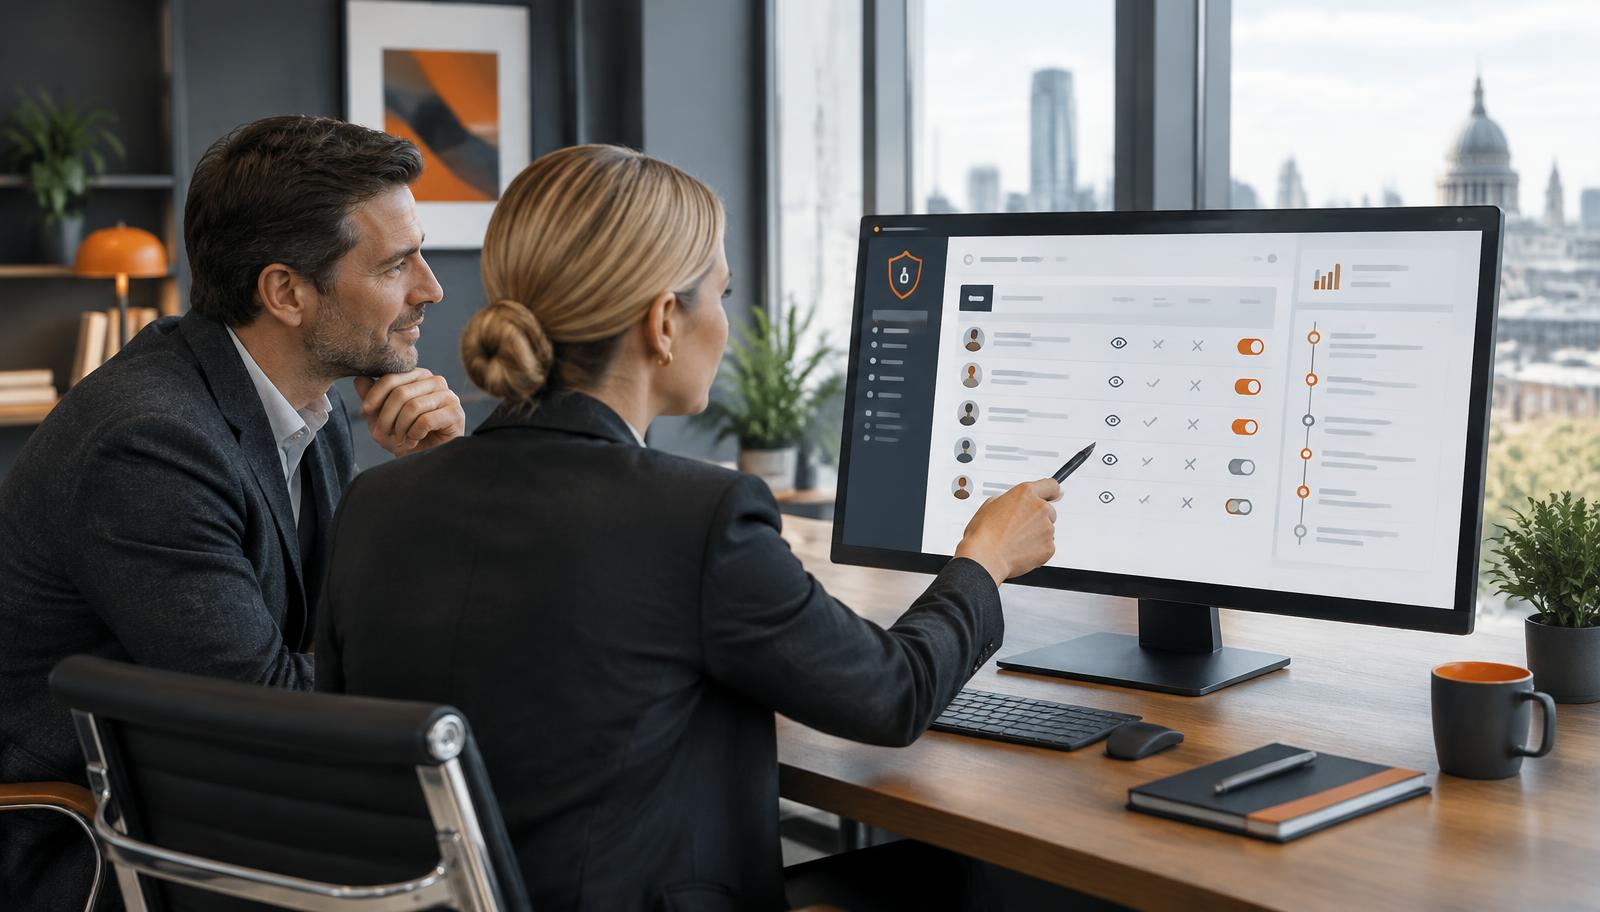
Security is not one feature. It is a connected set of controls covering the journey from a user's sign-in, through the application, to the database and every external service.
Published systems and custom domains use managed HTTPS certificates and TLS 1.2 or newer, protecting data in transit without relying on users to configure it.
Business data is held in a managed database with encryption at rest, controlled access and daily database backups retained for approximately 14 days.
Sign-in, account sessions and password recovery use a dedicated authentication service, with social sign-in available where appropriate.
Private API keys and service credentials are kept in encrypted secret storage and used on the server, rather than being embedded in pages sent to a user's browser.
Automated checks review software dependencies, database policies, exposed functions, access controls and common code-level risks throughout delivery.
Published systems can be monitored for important visitor errors and code issues, helping us identify and investigate problems rather than waiting for users to report them.
Independent assurance
Monitoring and secure engineering matter operationally. Independent verification gives procurement teams and larger customers additional confidence that recognised controls have been tested rather than simply described.
Organisation verified
Essential Systems is independently Cyber Essentials Plus certified. This verifies that our business devices, accounts and working practices meet recognised UK cyber security requirements within the scope of the certification.
Platform independently tested
Our reusable Business Operations System foundation has undergone independent penetration testing. Additional testing can be commissioned when a particular system handles especially sensitive information or has specific contractual needs.
Defence in depth
No single control carries the whole burden. Strong security comes from overlapping safeguards, careful configuration and responsible day-to-day operation.
Clear responsibilities
We avoid vague promises. The technical foundation provides strong safeguards, we shape them for your system, and your business retains an important role in using it securely.
Honest assurance
A secure platform is an essential starting point, but it does not remove the need for careful design. The sensitivity of your data, integrations, user roles and operational processes all affect the final risk profile.
Automated scanning can identify important weaknesses, but it cannot guarantee that any application is completely secure. Our Cyber Essentials Plus certification applies to Essential Systems, and our independent penetration test applies to the reusable core platform; neither should be read as a guarantee or as certification of every customer system.
If your organisation has contractual, insurance, data-residency or sector-specific requirements, we establish those during discovery and agree any additional independent assurance before the relevant information is brought into the system.
Production target standard
We are standardising the following controls across production systems. The precise combination remains subject to each application, its domain setup and the sensitivity of the information it processes.
Customer security pack
Customers can request a concise security and data-protection pack containing the information relevant to their system. Sensitive technical detail is shared through an appropriate review process rather than published openly.
Security questions
Connections to a published system are protected using HTTPS and modern TLS encryption. This protects information while it travels between a user's device and the system.
The managed database service also provides encryption for stored database data. Where a system connects to another service, we use secure server-side connections and keep private credentials out of the browser.
Yes. Access can be designed around roles and responsibilities, so a person sees only the records and actions needed for their work. Rules can be applied at the data level, not just by hiding a screen or menu item.
For example, an engineer might see assigned visits while a manager sees the wider operation. Administrative permissions are kept separate from ordinary user access.
Systems can use managed email sign-in and, where appropriate, social sign-in. Password handling is provided by the managed authentication service rather than being improvised inside the application.
Additional options can include password-reset controls and checking for known compromised passwords. The exact sign-in policy is agreed for each system; specialist corporate identity requirements are scoped separately.
Yes. The professional delivery environment includes automated checks for vulnerable software dependencies, database access rules and common application security issues. Deeper code and access-control reviews are also available during development and before important releases.
Essential Systems is Cyber Essentials Plus certified, and our reusable core platform has undergone independent penetration testing. Automated scanning remains a valuable safety net, but no scanner or test can guarantee that a system is completely secure.
The managed database is backed up daily, with a rolling retention period of approximately 14 days. This supports database recovery when required.
Uploaded files are stored separately from database backups, so file retention and recovery requirements should be agreed as part of the system design. We make that distinction clear rather than implying that every file is covered by a database restore.
No technology platform can make a business compliant by itself. Security controls support good governance, but compliance also depends on what information you collect, why you collect it, who has access, how long it is retained and how your team works.
During discovery we identify sensitive workflows and can design appropriate access, retention and audit requirements. Our organisational certification and core-platform testing provide a strong baseline; additional system-specific testing or legal assurance is scoped where the information or contractual requirements justify it.
Tell us what information the system will hold, who needs access and which obligations matter to your business. We can then design the workflow and its safeguards together, rather than trying to retrofit security later.
Your information stays confidential. We are happy to sign an NDA before any detailed discussion.